MFA doesn't stop session cookie replay. Endpoint detection doesn't catch fileless malware without behavioral analysis. Here's the full post-phishing kill chain and what actually stops it.
Resources
Blog
Blog
Keep up to date with the latest offensive security news, knowledge, and resources.
Step-by-step walkthrough of cracking NTLMv1-SSP hashes with rainbow tables, including how to coerce auth, disable ESS, recover NT hashes, and remediate.
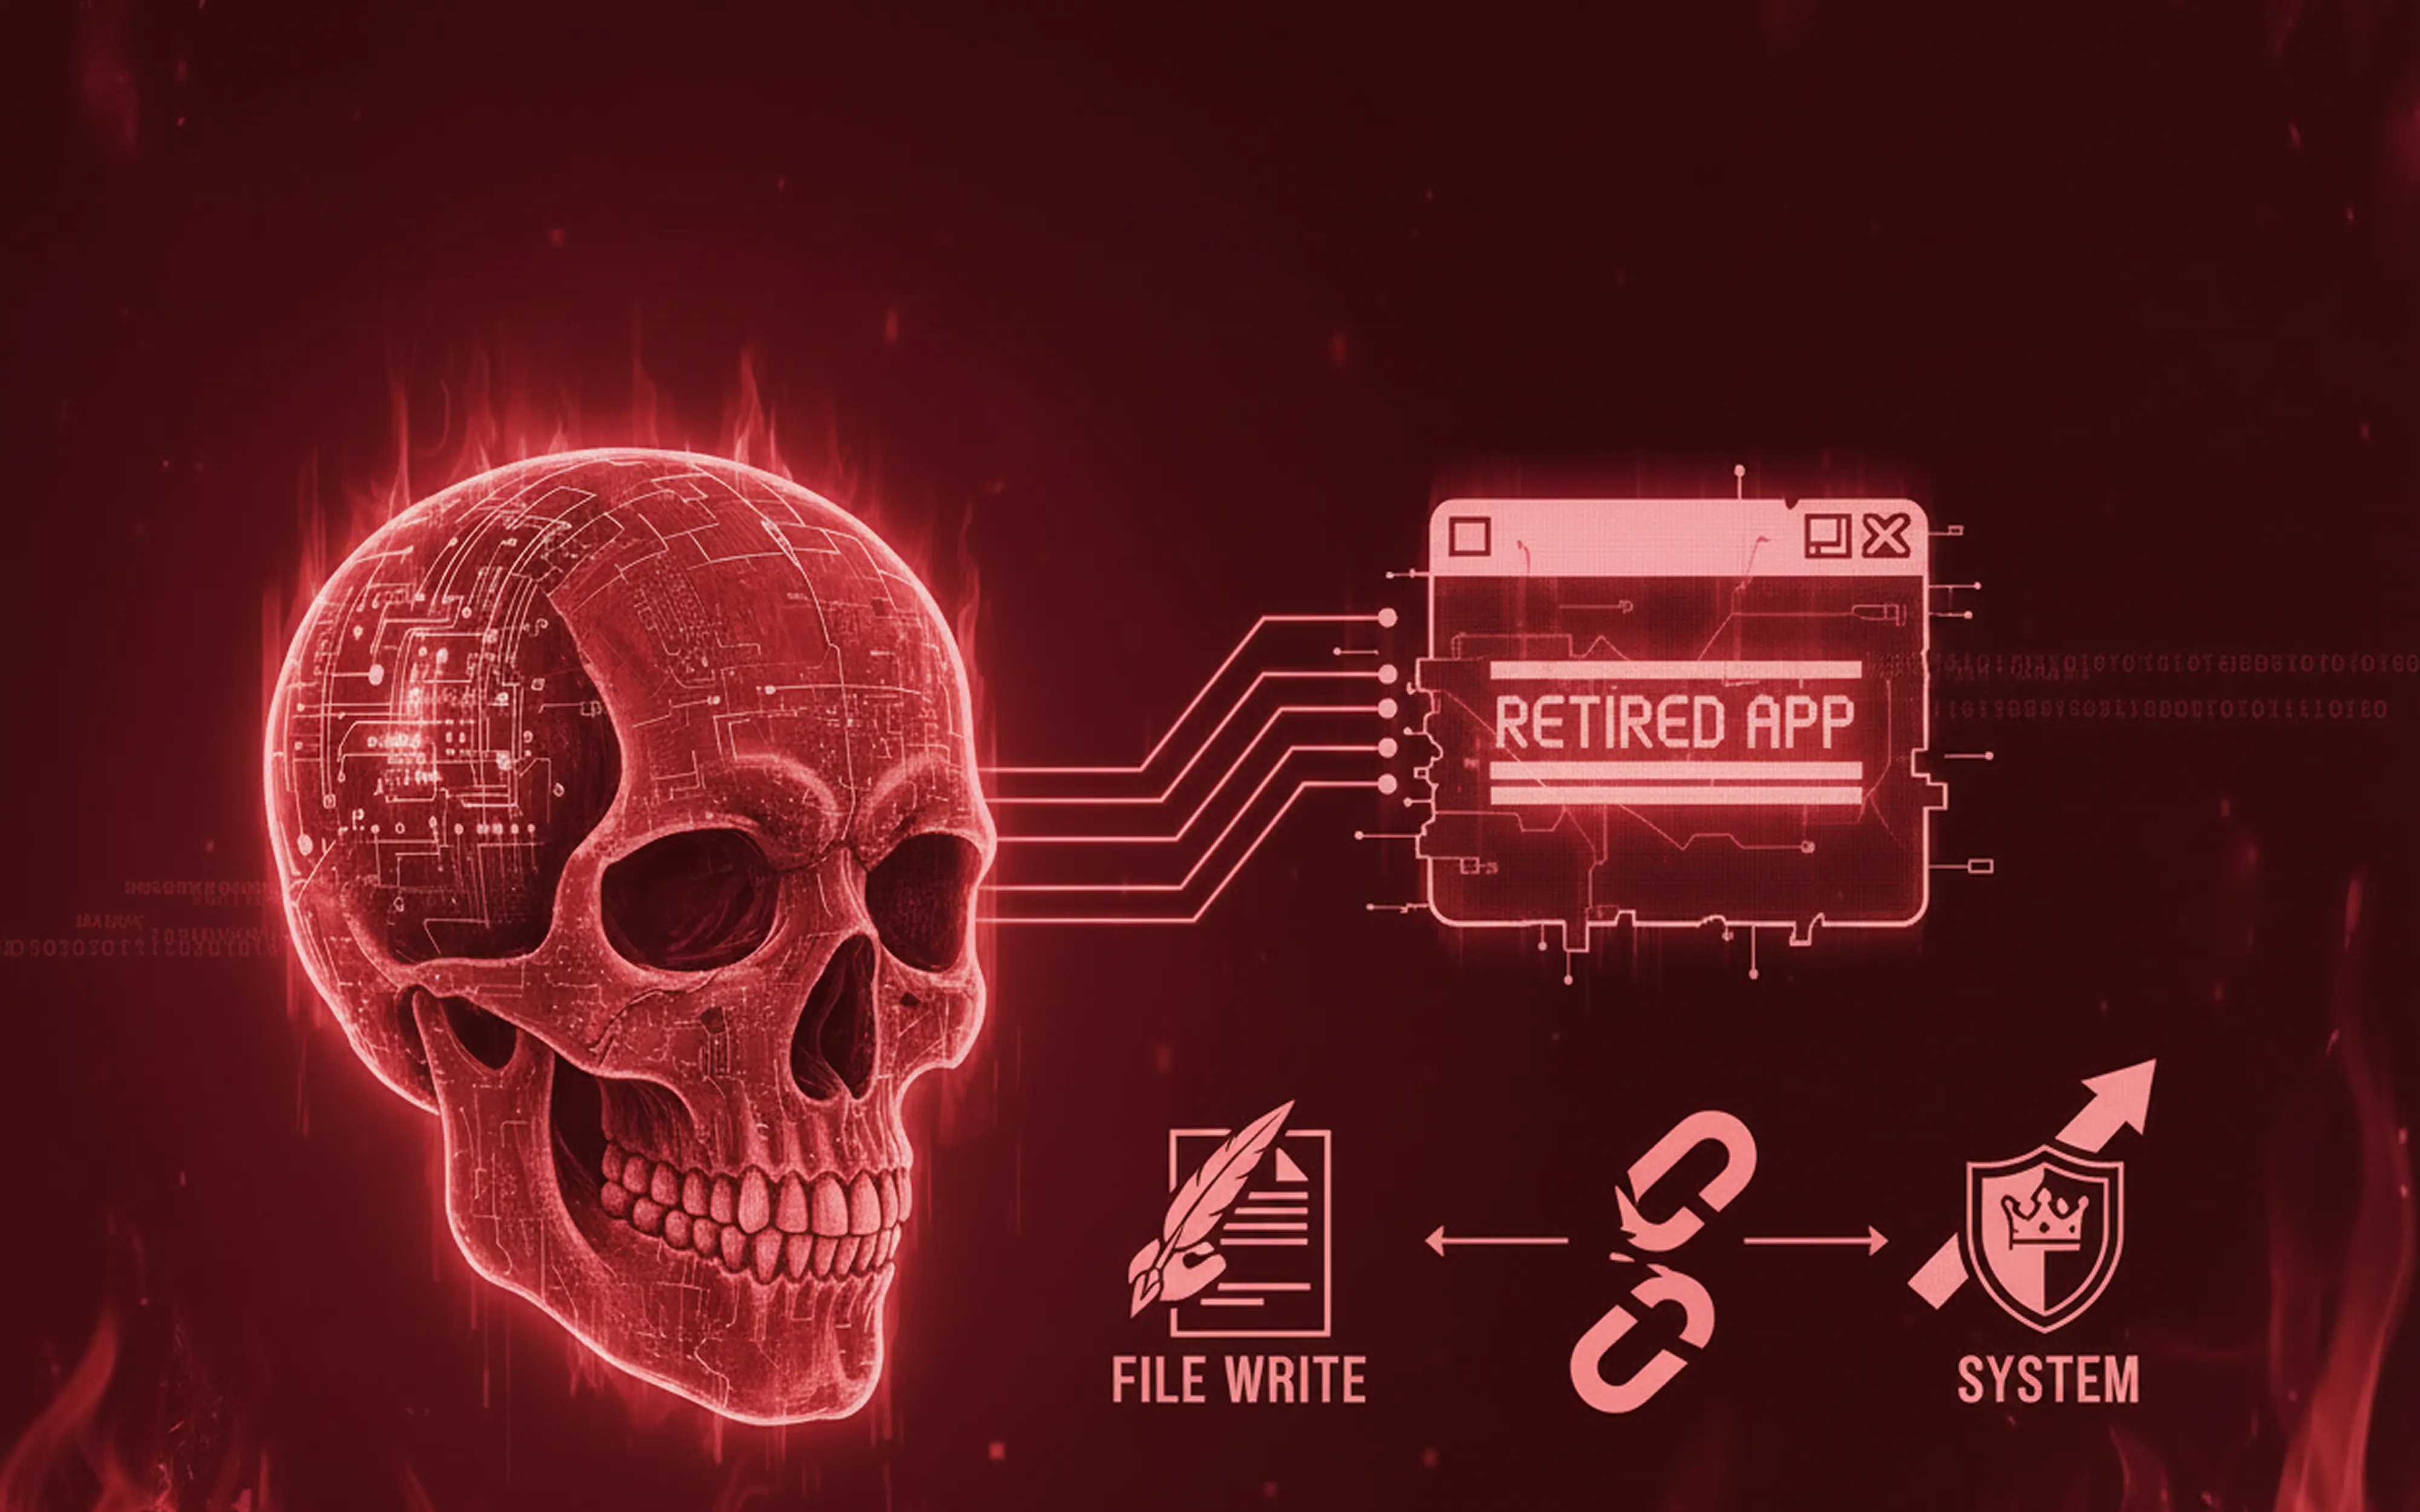
Discover how an unsanitized file write endpoint in Omega Enterprise Gateway escalates to SYSTEM-level code execution and what dead code reveals about real-world security bugs.
A successful prompt hack looks like your system working correctly for someone else. The mechanism that makes this possible is the same one you’re paying for.
Attackers are using a fake Microsoft support page to deliver password-stealing malware disguised as a Windows update and antivirus tools missed it entirely. Learn how the attack works and what your team can do to stay protected.
Andy Grant explores what happens when you remove time-boxes, checklists, and rigid scope from offensive security and trust skilled engineers to follow their intuition.
