Unauthenticated SQL injection in mJobTime (CVE-2026-9209) exposes construction and field services data. No vendor fix exists after 120-day disclosure.
Resources
Blog
Penetration Testing
Keep up to date with the latest offensive security news, knowledge, and resources.
Preparing for a penetration test? This checklist will inform you on what to expect and what steps you should take to get the most out of your organization’s upcoming pentest.
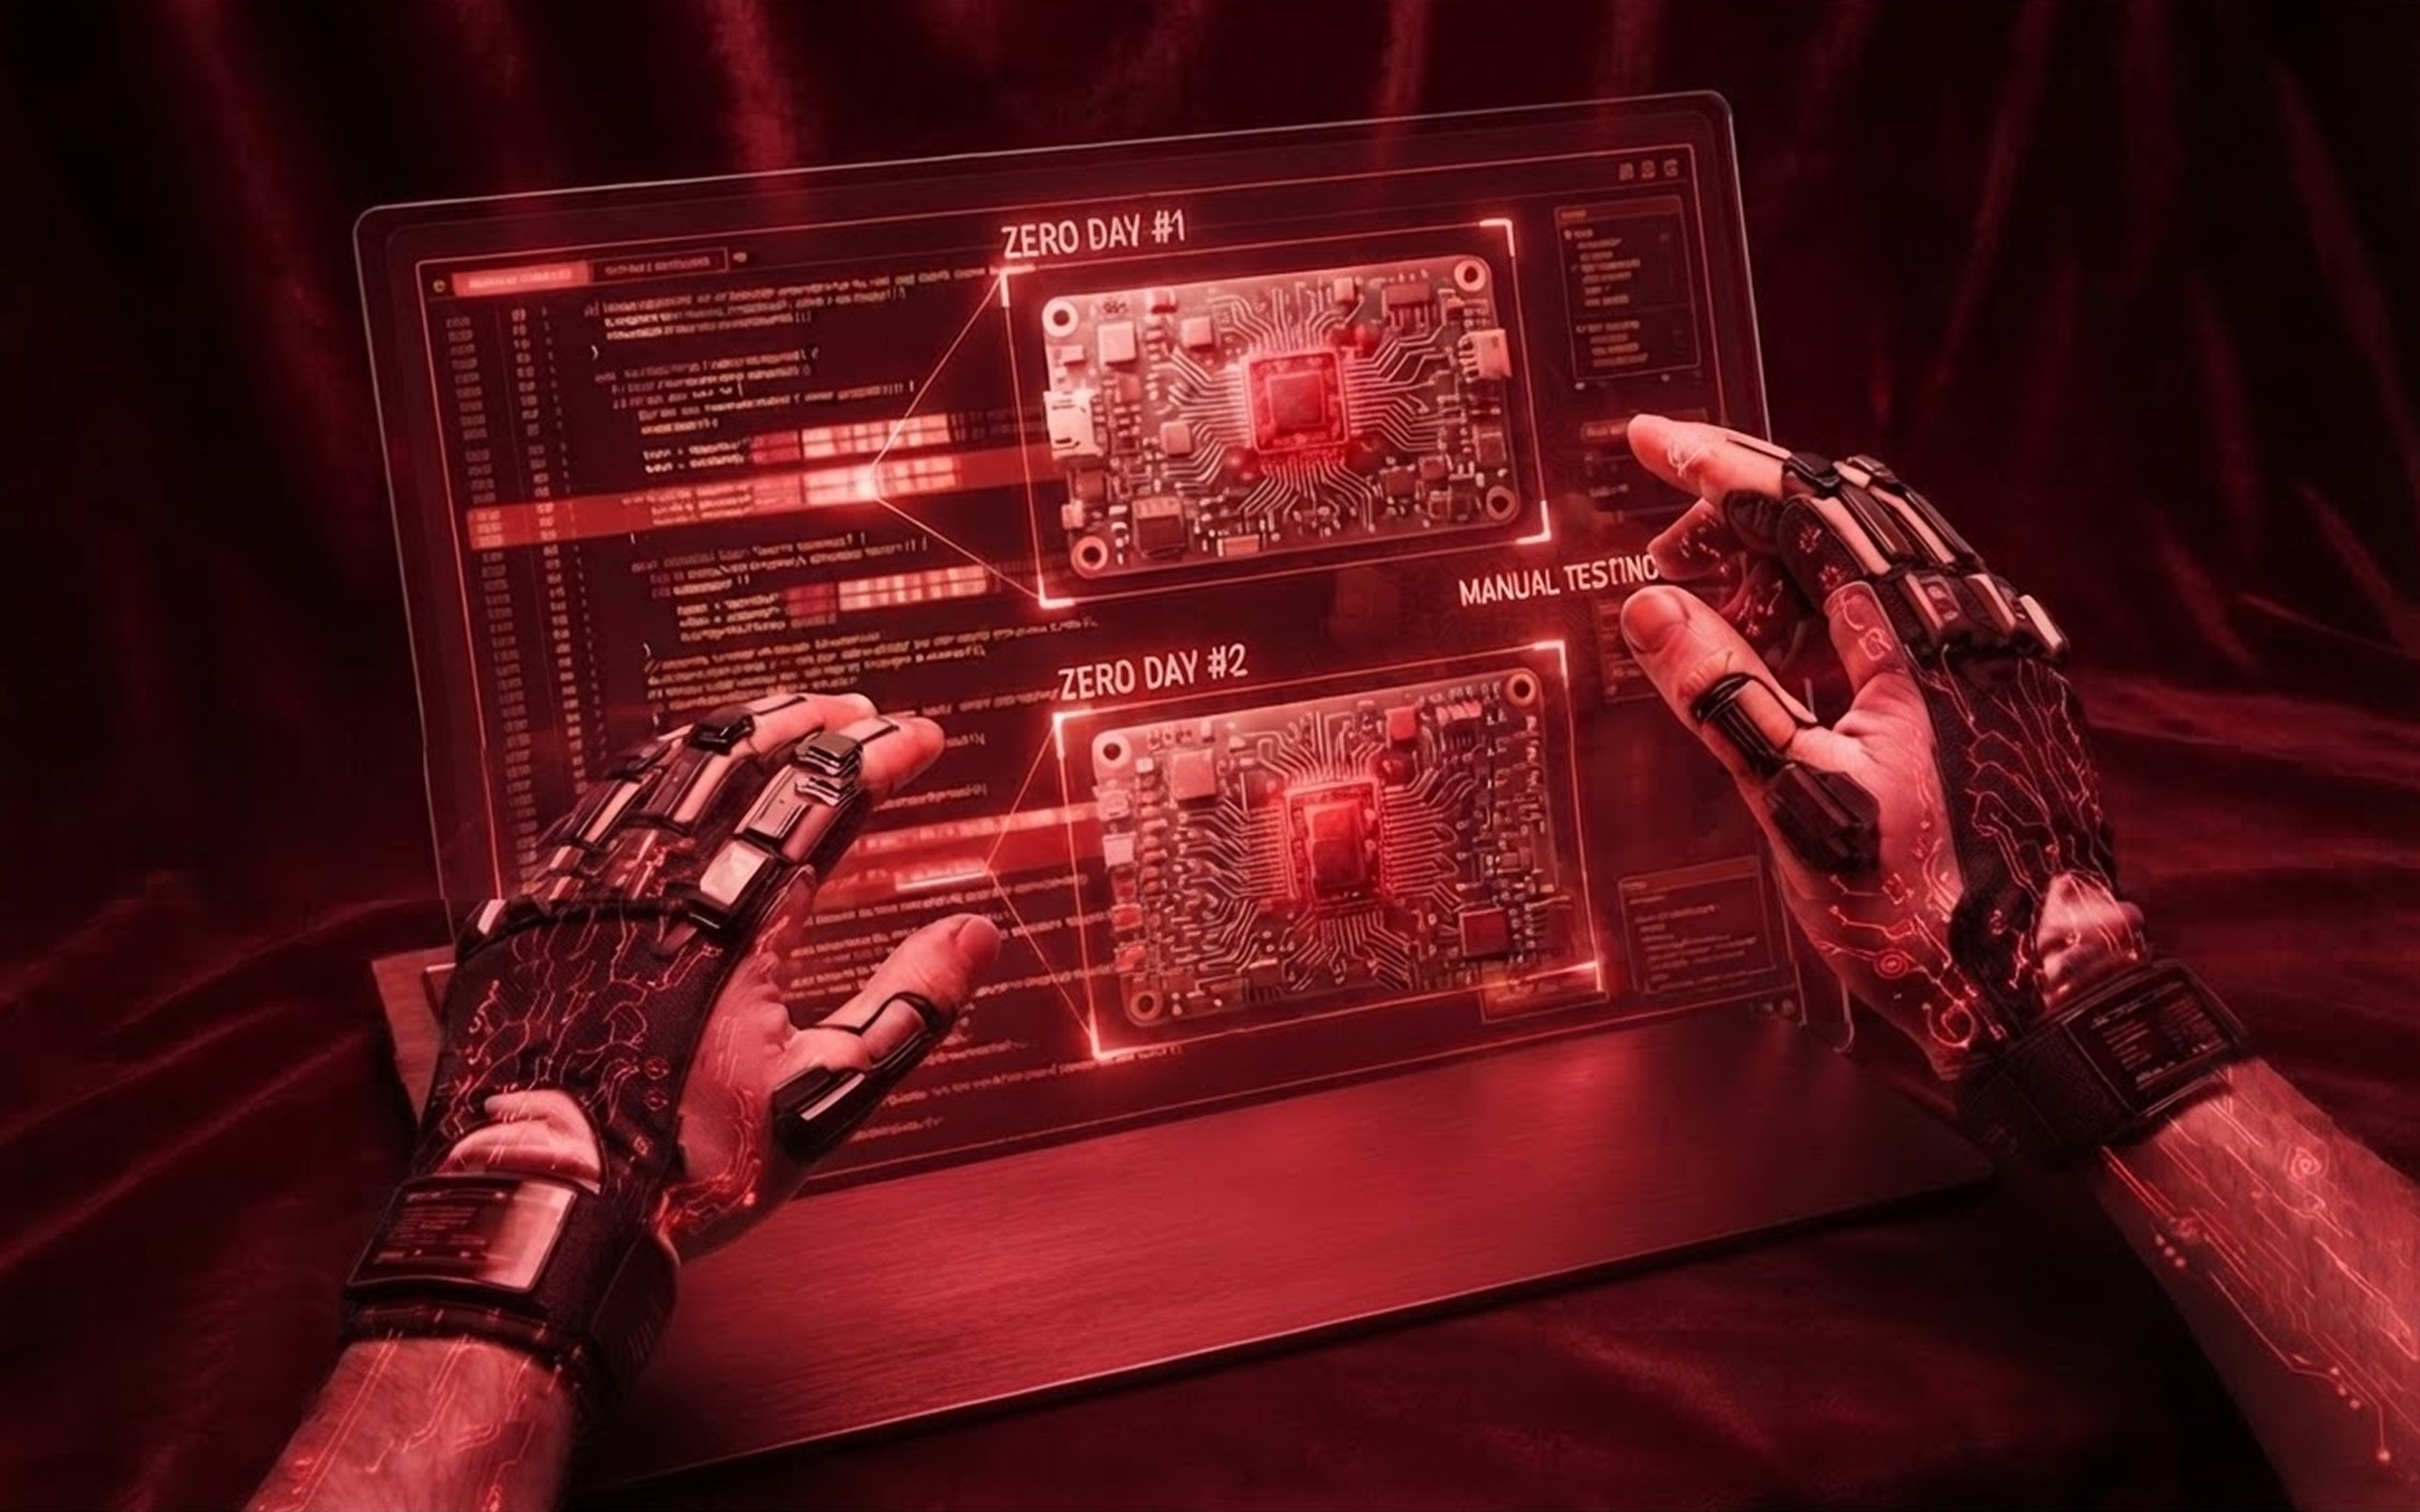
Apex, one of Sprocket's AI agents, found a session injection flaw in minutes. Human testers chained it into two zero-days.
Explore the top 10 CPTaaS companies in 2026. Compare continuous penetration testing platforms, PTaaS providers, ASM capabilities, compliance support, and human-led testing models.
MFA doesn't stop session cookie replay. Endpoint detection doesn't catch fileless malware without behavioral analysis. Here's the full post-phishing kill chain and what actually stops it.
Step-by-step walkthrough of cracking NTLMv1-SSP hashes with rainbow tables, including how to coerce auth, disable ESS, recover NT hashes, and remediate.
