Step-by-step walkthrough of cracking NTLMv1-SSP hashes with rainbow tables, including how to coerce auth, disable ESS, recover NT hashes, and remediate.
Resources
Blog
Penetration Testing
Keep up to date with the latest offensive security news, knowledge, and resources.
Discover how an unsanitized file write endpoint in Omega Enterprise Gateway escalates to SYSTEM-level code execution and what dead code reveals about real-world security bugs.
Legacy healthcare systems can’t be patched but they can’t be ignored. Learn how to pentest around clinical assets without disrupting patient care.
Multifunction printers silently store domain credentials, expose unauthenticated management interfaces, and sit on flat networks. Learn how attackers exploit MFPs to achieve domain admin in minutes.
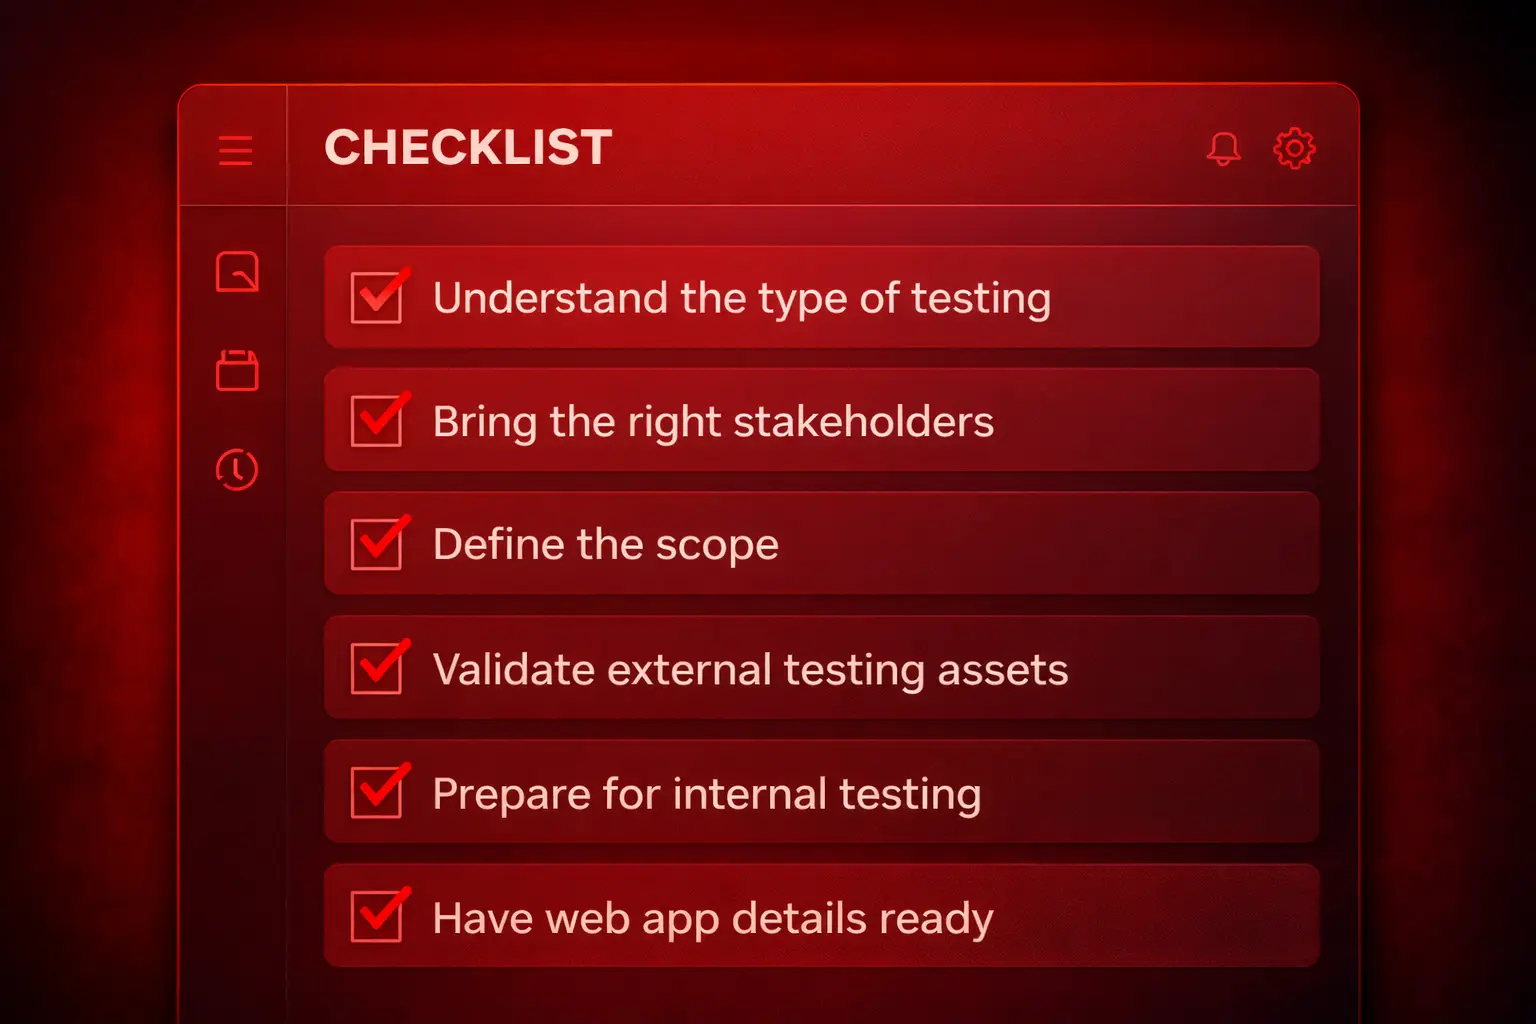
The fastest path from kickoff to testing starts with alignment, preparation, and the right people in the room.
Know what a HIPAA auditor will ask for before they show up. A tier-by-tier breakdown of the security evidence that separates audit-ready organizations from the rest.
