OWASP’s 2025 Top 10 shows how security misconfigurations and software supply chain issues dominate. Here’s how continuous pentesting closes the gap.
Resources
Blog
Offensive Security
Keep up to date with the latest offensive security news, knowledge, and resources.

Rotating pentesters every year may sound like getting “fresh eyes,” but it often resets progress and weakens security maturity. Learn why continuity-based penetration testing, anchored in frameworks like MITRE ATT&CK and iterative feedback loops, drives deeper insight, faster remediation, and stronger defenses over time.
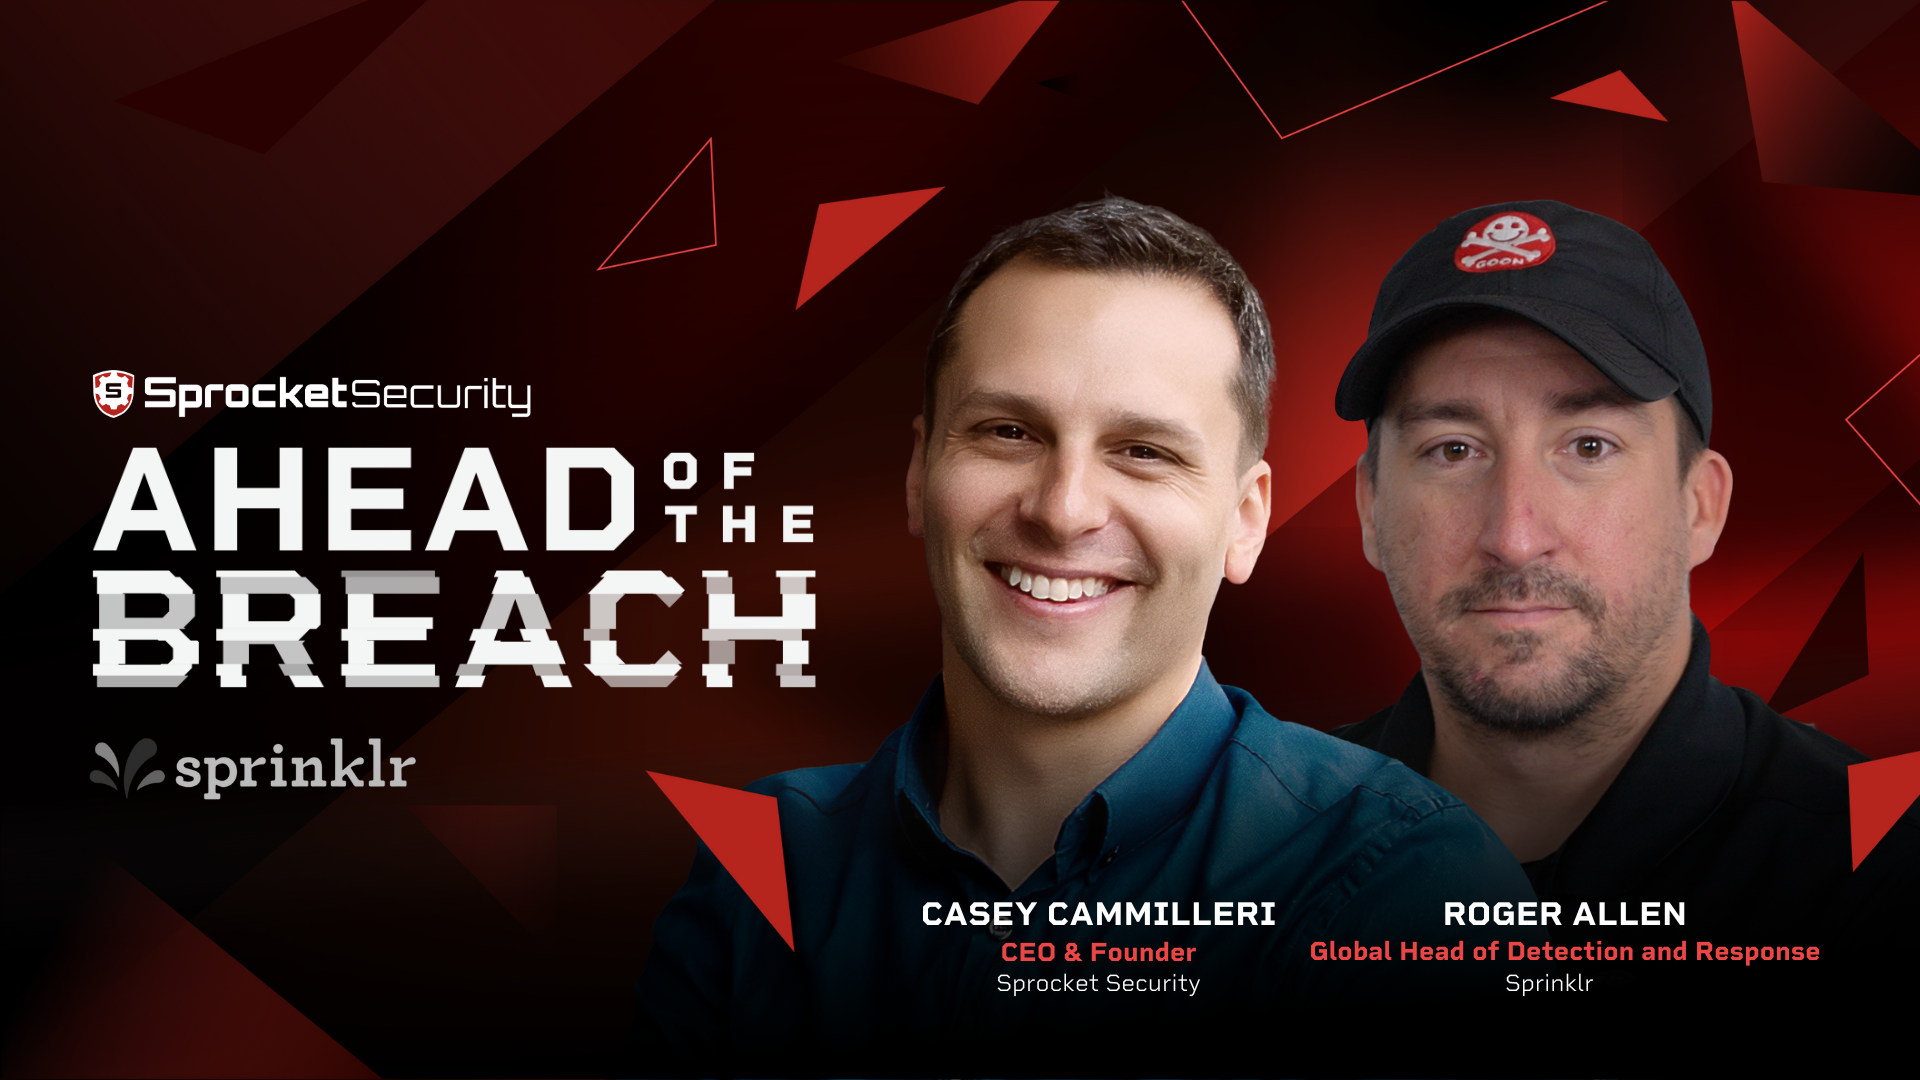
Most security programs fail because they focus only on reactive detection while sidelining proactive measures. Roger Allen, Sr. Director, Global Head of Detection & Response at Sprinklr, explains why vendor telemetry gets you 90% of the way there.
In today's episode, Casey addresses why continuous pentesting is a must for dynamic environments.
What if you could predict which vulnerabilities threat actors will weaponize months before CISA adds them to their Known Exploited Vulnerabilities list? Andrew Grealy, Head of Armis Labs, has built exactly that capability, providing organizations with threat intelligence that arrives 3-12 months ahead of traditional indicators.
In today's episode, Casey addresses how to build an offensive security program from scratch.
